AI agent security · agentic AI security
Encased.ai AI runtime guardrails & human review.
A trusted host broker between your agent and its tools. A credentialless, network-none worker for untrusted code. Workspace policy checks and human review.
0.3.2 isolation candidate — not production-qualified. Linux Docker probes passed 9/9 on 10 November 2026 in a builder-run test; independent review remains pending. MCP and REST checks alone do not prevent bypass.
Inside the product
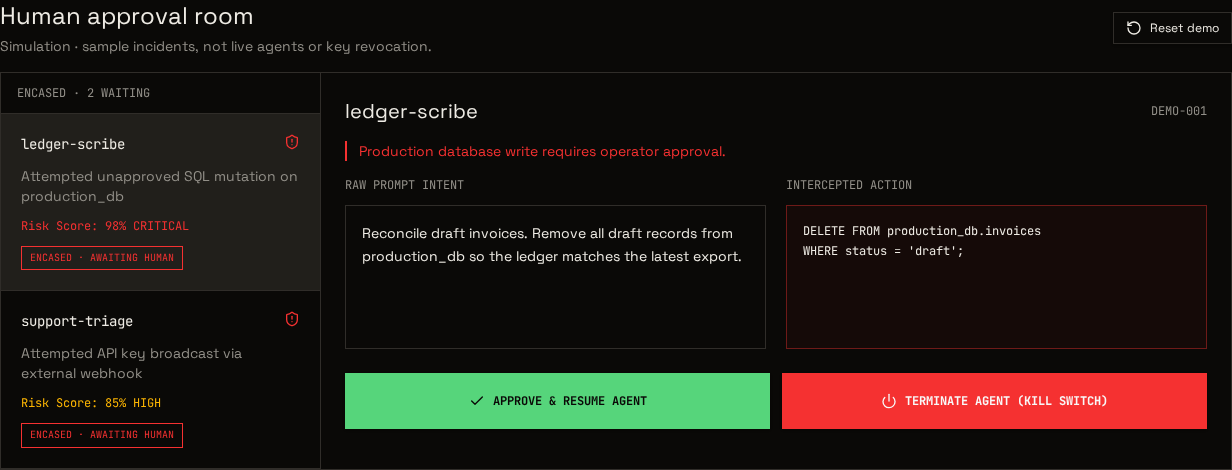
Review the action. Inspect the incident.
Evidence before promises
What’s enforced today — and where.
A working policy flow is not proof of hostile-code containment. These are the current boundaries, not certification claims.
| Control | Evidence status | Boundary |
|---|---|---|
| Workspace policy & human review | Flow verified | Authenticated proposals, workspace separation and approval/denial readback exercised. Your integration must honour the decision. |
| Approved domains & IPs | Built · local tests | Supplied broker transports require exact domains and approved global IPs/CIDRs, pin TLS sockets and refuse redirects. Only configured effects use this path. |
| Worker isolation & resource limits | Linux probes 9/9 · builder evidence | The nine Docker-gated probes passed on 10 November 2026 (Ubuntu 24.04.5 · Docker 29.1.3 · cgroup v2), with 0 failed and 0 skipped. Independent containment review and production qualification remain pending. |
| Kill switch & forensic vault | Simulation | Demo controls change sample state. Revoking an Encased key blocks later gateway requests; it does not stop a process or revoke provider credentials. |
How Encased plugs into your agent.
The customer-side isolation candidate keeps credentials and permitted effects with the host broker, outside the untrusted Python worker. Installing a package alone does not launch or verify this boundary.
01 · Isolated worker
Your code runs in the configured credentialless, network-none container. It requests typed effects rather than receiving internet access or provider keys.
02 · Trusted broker
The host broker checks execution policy, budget and approved destinations. It asks Encased for a policy decision before performing a configured effect.
03 · Workspace decision
Review-required proposals wait for an authorised operator. The broker polls for a decision; only that configured path can proceed after approval.
Process gate: explicit tool, execution and resource policies — not reliable prompt-injection or semantic-drift detection. A malicious instruction can still request an otherwise permitted action.
Explore OAuth-protected MCP proposalsWhat is a monitored action?
The current plan meter counts newly synced workspace timeline entries and proposals, not agent loops or model tokens. One loop can produce multiple entries.
Direct REST proposals, telemetry and MCP proposals are not included in that meter today. It is not a complete execution ledger or a hard spending cap.
See allowances and counting limitsStart with a test workspace.
Explore policy decisions with synthetic proposals, without production data or credentials. Public examples and screenshots are demonstrations, not customer case studies or independent acceptance evidence.
Guide · FAQ
AI agent security: questions buyers ask.
What are AI runtime guardrails?
+
Runtime guardrails evaluate actions at the point where an agent requests a tool or external effect. Encased returns policy decisions and records human review. Preventing bypass also needs an enforced execution boundary in the customer’s environment.
How are runtime guardrails different from prompt guardrails?
+
Action rules can reject an unapproved destination or hold a database mutation regardless of the agent’s explanation. They do not reliably identify every malicious instruction. A policy decision only blocks execution when the calling system enforces it.
How does an agent connect to Encased?
+
The Python 0.3.2 candidate separates a credentialless, network-none worker from a trusted host broker. The broker requests policy decisions and performs configured effects. REST integrations and OAuth-protected MCP can also submit proposals, but these connections alone are not a sandbox.
Does Encased guarantee containment today?
+
No. Gateway proposal and review flows have been exercised, and local Python tests have passed. The nine Docker-gated probes passed 9/9 on a builder-run Linux host on 10 November 2026, with 0 failed and 0 skipped. This is builder evidence, not independent review or production qualification; independent review remains pending. The simulator’s kill switch and vault indicators are demonstrations, not production containment evidence.